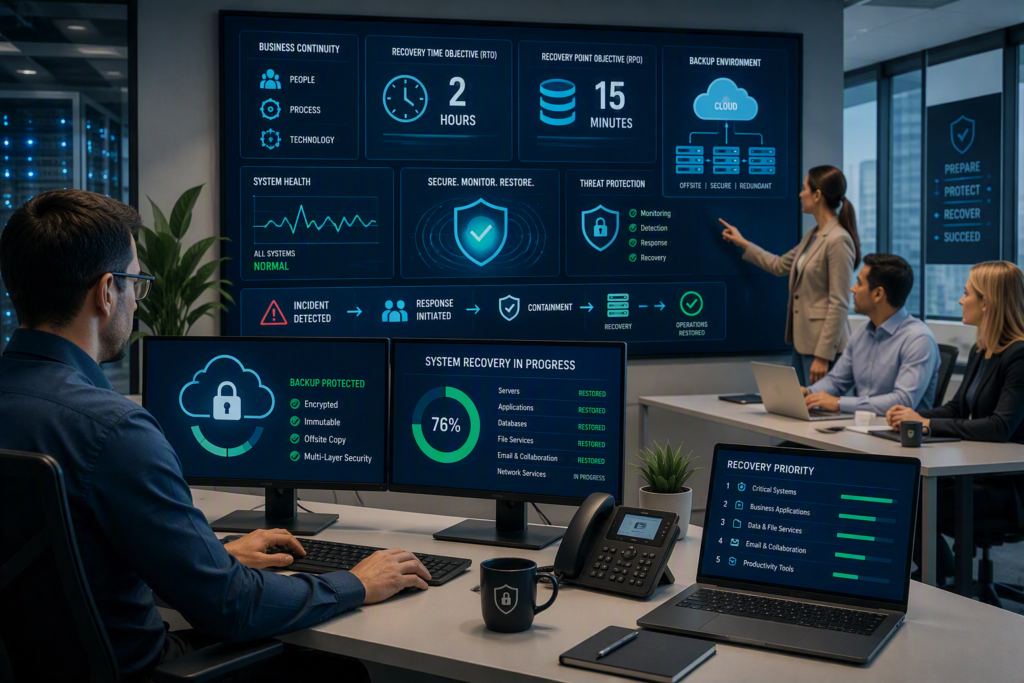
For a healthcare office, professional firm, nonprofit, or local business, even a few hours of downtime can affect revenue, customer service, productivity, and trust.
An IT disaster recovery plan gives your business a clear process for responding to technology failures and restoring critical systems. Instead of trying to figure out what to do during an emergency, your team already knows what needs to happen, who is responsible, and which systems need to be restored first.
The goal is not to predict every possible disaster. It is to prepare for the most important risks and create a practical recovery process your business can actually follow.
What Is an IT Disaster Recovery Plan?
An IT disaster recovery plan explains how your organization will restore technology, systems, applications, and data after a major disruption.
Disaster recovery is closely connected to business continuity, but they are not the same thing.
Business continuity focuses on how your organization will continue serving customers and performing essential work during a disruption.
Disaster recovery focuses on restoring the technology that makes that work possible.
For example, if your server fails, business continuity may involve employees working from another location or using temporary processes. Disaster recovery involves restoring the server, applications, data, and network access needed to return to normal operations.
A backup alone is not a disaster recovery plan. You may have copies of your files, but that does not automatically mean your business can recover quickly.
Someone still needs to know:
What needs to be restored first
Where the backups are stored
How to access the backups
Who is authorized to start the recovery
How systems will be rebuilt
Which vendors need to be contacted
How employees and customers will be informed
How long each system can remain unavailable
A good IT disaster recovery plan connects all of these pieces.
Start With Your Business, Not Your Technology
One of the biggest mistakes businesses make is starting disaster recovery planning with technology instead of business operations.
Start by asking a simple question:
What would stop your business from operating if it disappeared today?
Talk to department leaders and identify the systems employees depend on every day.
For example, an accounting firm may depend on:
Practice management software
Secure client files
Email
Internet access
Accounting applications
Phone systems
A medical office may prioritize:
Patient scheduling
Electronic records
Phones
Payment processing
Secure communications
A nonprofit may depend heavily on:
Donor databases
Email
Online fundraising systems
Shared documents
Communication platforms
Once you identify these systems, you can decide how quickly each one needs to be restored.
This process is often called a business impact analysis. It helps your organization understand the operational and financial effects of technology downtime and set realistic recovery priorities.
Understand Recovery Time Objectives
A Recovery Time Objective (RTO) defines how long your business can reasonably operate without a particular system.
For example, your business may be able to operate for several hours without access to archived documents, but losing your phone system for the same amount of time could have a much greater impact.
Your recovery priorities should reflect that difference.
Some systems may need to be restored within an hour. Others may have a recovery target of four hours, one business day, or longer.
There is also a cost factor. Faster recovery usually requires additional technology, redundancy, cloud services, monitoring, or infrastructure.
The goal is to choose recovery times that make sense for your business rather than trying to restore everything instantly.
Understand Recovery Point Objectives
A Recovery Point Objective (RPO) determines how much recent data your business can afford to lose.
Consider a company that backs up important files once every night.
If a major failure happens at 4:00 p.m., the business could potentially lose the day’s work.
More frequent backups can reduce this potential data loss.
For example:
Daily backups may be suitable for some low-priority information
Hourly backups may be appropriate for important operational data
Near-continuous protection may be needed for highly critical systems
Your RPO should be based on the value of the information and the effect that data loss would have on your business.
Together, your RTO and RPO help determine the backup, recovery, and infrastructure your organization actually needs.
Document Your IT Disaster Recovery Process
When an emergency happens, your recovery plan should be easy to understand.
Avoid creating a massive technical document that only one IT employee knows how to use. Your plan should clearly explain what needs to happen and who is responsible.
Keep an emergency copy of the plan somewhere that remains accessible if your primary network or office is unavailable. This may include a secure offline copy and printed emergency contact information.
Your plan should include:
Critical systems and their recovery priority
The person responsible for each system
Key software and technology vendors
Internet and phone provider contact information
Backup locations and retention information
Hardware and network details
Firewall and server information
Replacement equipment options
Emergency communication procedures
Staff and customer notification procedures
Recovery instructions for critical applications
Do not assume that important contact information will be available inside the system that has failed.
The same applies to passwords and administrative access. Use a secure password management process and establish emergency access procedures for authorized personnel.
Review these details whenever employees leave, responsibilities change, or new systems are introduced.
Build Backups That Support Real Recovery
Backups are one of the most important parts of an IT disaster recovery plan, but simply having backups is not enough.
Your backup strategy should consider:
What data needs to be backed up
How frequently it should be backed up
How long backups should be retained
Where backups are stored
Who can access them
Whether backups can be deleted or changed
How quickly the data can be restored
Whether the restored data can actually be used
Keeping multiple copies of important information, including a protected copy separate from your main environment, can improve your ability to recover from a serious incident.
This is particularly important with ransomware.
If an attacker gains access to administrative accounts, they may also attempt to access or delete backups. Separate backup credentials, multifactor authentication, restricted permissions, and protected or immutable backup copies can add important layers of protection.
It is also important to understand what your backups actually contain.
Backing up documents may not be enough if your business also depends on application databases, system configurations, specialized software, or other technology settings.
Your recovery plan should answer a simple question:
If this system disappeared today, could we actually rebuild it from our backups?
Do Not Assume Cloud Storage Is a Complete Backup
Many businesses use Microsoft 365, cloud applications, hosted software, and cloud file storage every day.
Cloud services provide important benefits, but cloud storage should not automatically be treated as a complete backup strategy.
Deleted files, compromised accounts, synchronization problems, retention settings, and account access issues can all affect your ability to recover information.
Review each important cloud service separately.
Consider:
What information is stored there?
How long are deleted items retained?
Can administrators restore data?
What happens if an account is compromised?
Is there an independent backup?
How quickly can important information be recovered?
A strong disaster recovery strategy protects the systems your business actually depends on, whether those systems are located in your office, hosted in the cloud, or managed by a third-party provider.
Test Your IT Disaster Recovery Plan
A disaster recovery plan that has never been tested is an assumption, not a reliable recovery process.
Testing does not mean you have to shut down your business for an entire day.
Start with a simple tabletop exercise.
Bring together the people responsible for responding to an emergency and walk through a realistic situation.
For example:
Your main server suddenly stops working at 10:00 a.m. What happens next?
Ask:
Who declares the incident?
Who contacts your IT provider?
What systems need to be restored first?
What happens if the office has no internet?
Can employees work remotely?
How will staff communicate?
How will customers be informed?
Where are your backups?
Who can access them?
How long should recovery take?
Then test the technical side.
Restore sample files. Check backup access. Test a workstation recovery. If possible, practice restoring a critical application in a safe environment.
Most importantly, verify that the restored information actually works.
A file that exists but cannot be opened is not a successful recovery.
Update Your Plan Regularly
Your business changes over time.
Employees leave. New employees join. Software changes. Cloud services are added. Offices move. Equipment is replaced. Vendors change.
Each of these changes can affect your recovery plan.
Review your IT disaster recovery plan at least once a year and update it after major technology or business changes.
After a real incident or recovery test, document what worked and what did not.
Use those lessons to improve the plan.
Regular testing and maintenance can help ensure that your recovery process remains useful when you actually need it.
Assign Clear Roles During an Emergency
During a technology emergency, employees should not have to guess who is responsible.
Assign clear roles before a disaster occurs.
For example:
Business lead: Makes business decisions and coordinates the overall response.
IT lead: Coordinates technical troubleshooting, containment, and recovery.
Communications lead: Keeps employees, customers, vendors, and other stakeholders informed.
Vendor contact: Communicates with software providers, internet providers, phone companies, and other third parties.
In a small business, one person may have several responsibilities. That is fine, but there should still be a backup person who can step in if the primary contact is unavailable.
Your plan should also identify when other professionals need to be contacted.
A cybersecurity incident may require involvement from your insurance provider, legal counsel, cybersecurity professionals, or other specialists. The response to ransomware or a suspected data breach may be different from the response to a simple hardware failure.
Do not immediately restore compromised systems before determining whether additional investigation or evidence preservation is required.
Work With an IT Partner You Can Reach When You Need Help
Many small and mid-sized businesses do not have a full internal IT department.
A managed IT provider can help your organization identify critical systems, review backup strategies, document recovery procedures, monitor technology, and prepare for unexpected outages.
The goal is not simply to create a document.
The goal is to create a recovery process that works for your people, your technology, and your business.
At Myriad Technologies, we help businesses understand their technology risks and build practical IT strategies around their operations, budget, and recovery needs.
Start Your IT Disaster Recovery Plan Today
You do not need to build a complicated disaster recovery plan in one day.
Start with one critical system.
Ask:
What would happen if this system disappeared this afternoon?
Then identify:
What data you need to recover
Where your backup is stored
Who is responsible for recovery
How quickly the system needs to return
How employees would continue working while it is unavailable
That simple exercise can reveal gaps you may not have considered.
An IT disaster recovery plan is most valuable before a disaster happens. By planning ahead, testing your backups, assigning responsibilities, and reviewing your recovery process regularly, your business can be better prepared when technology suddenly stops working.
Need help creating a practical disaster recovery plan for your business? Contact Myriad Technologies to discuss your IT recovery, backup, and business continuity needs.