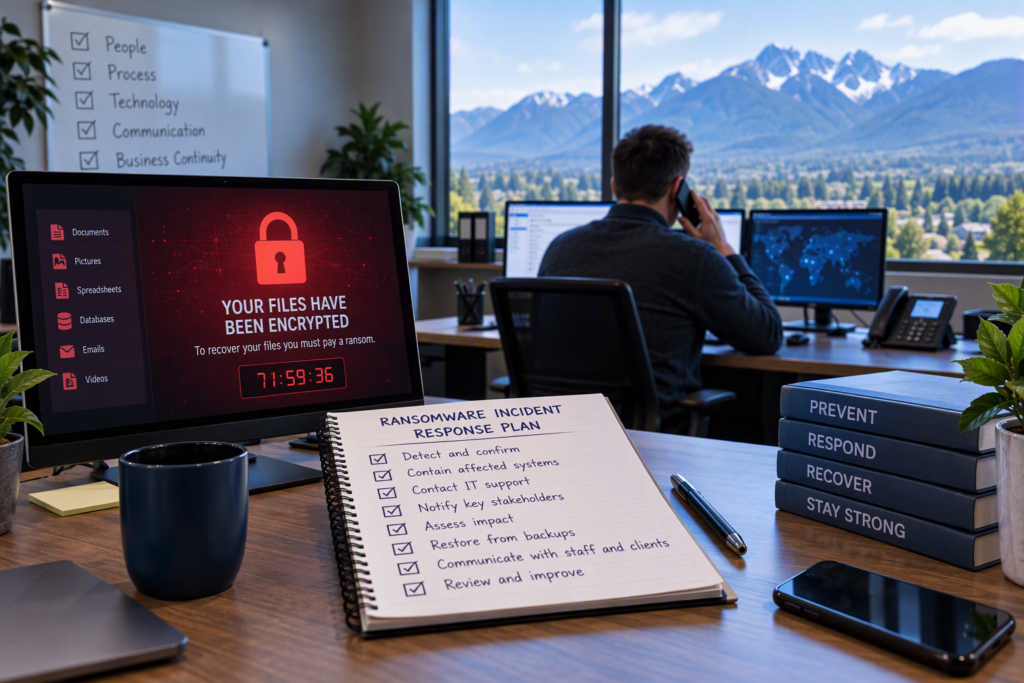
A ransomware attack can bring a Fraser Valley business to a standstill within hours. A single compromised laptop can provide attackers with a path into shared files, Microsoft 365 accounts, business applications, and other connected systems. Without a ransomware incident response plan, employees may waste valuable time trying to decide what to do while the attack continues.
For businesses in Chilliwack, Abbotsford, Langley, Mission, and throughout the Fraser Valley, ransomware protection should involve more than antivirus software and backups. Businesses also need a documented plan for detecting, containing, communicating, and recovering from a ransomware incident.
The Canadian Centre for Cyber Security reports that ransomware incidents affecting Canadian organizations have increased significantly in recent years. Its Ransomware Threat Outlook 2025–2027 reports an average 26% year-over-year increase in known Canadian ransomware incidents between 2021 and 2024 and states that organizations of all sizes remain at risk.
For a 20-person accounting firm, healthcare practice, nonprofit, construction company, or professional office, the practical question is simple: What happens if your systems are suddenly unavailable?
A ransomware incident response plan gives your team an answer before an emergency happens.
Why Ransomware Response Planning Matters for Small Businesses
Ransomware is no longer simply a problem for large corporations. The Canadian Centre for Cyber Security states that all Canadian organizations, regardless of size or sector, are at risk of ransomware. It also notes that organizations with fewer cybersecurity resources can face greater challenges responding to sophisticated attacks.
Large organizations may have dedicated security teams, legal departments, communications staff, and pre-arranged incident response providers. Many small and midsize businesses do not.
A typical small business may have an office manager, an external IT provider, cloud applications, shared files, and a collection of business-critical devices. When ransomware appears, there may be no obvious person responsible for making immediate decisions.
That is where a small business ransomware response plan becomes especially valuable.
A written plan should answer important questions before an attack occurs:
Who has authority to shut down or isolate systems?
Which computers or accounts should be disconnected first?
Who contacts the managed IT provider?
Who contacts the cyber insurance provider?
Who contacts legal counsel?
How are employees informed?
Who communicates with customers or affected individuals?
When does the business need to consider regulatory reporting?
How will systems and data be restored?
The goal is not to create a complicated emergency manual. It is to make sure everyone knows what to do during the first critical stages of a cybersecurity incident.
What Should a Ransomware Incident Response Plan Include?
A practical ransomware incident response plan should be short enough that employees can actually use it.
Start by identifying the people responsible for making decisions. Your plan should include a primary incident commander and a backup decision-maker who can authorize emergency actions if the primary contact is unavailable.
Keep critical contact information outside the affected network. Include your managed IT provider, cybersecurity provider, cyber insurance company, legal counsel, and other important vendors.
Your plan should also document your backup and recovery strategy. Backups should be monitored and tested regularly rather than simply assumed to work. The Canadian Cyber Centre identifies backups, multi-factor authentication, software updates, and phishing awareness as important baseline cybersecurity practices.
A basic ransomware response plan should include:
Incident commander: The person authorized to make urgent decisions.
Emergency contacts: IT provider, cybersecurity provider, cyber insurer, legal counsel, and relevant vendors.
System isolation procedures: Clear instructions for disconnecting affected devices or accounts.
Backup information: Location, protection, monitoring, and recovery procedures for business backups.
Communication procedures: Employee, customer, supplier, and stakeholder communication plans.
Regulatory considerations: A process for determining whether an incident creates reporting obligations.
Recovery procedures: Steps for restoring systems safely and verifying that the environment is secure.
Incident documentation: A record of what happened, what systems were affected, and what actions were taken.
The plan should be reviewed whenever your employees, technology environment, vendors, or insurance coverage changes.
Ransomware Prevention Should Be Part of the Plan
Incident response begins before ransomware reaches your network.
A good response plan should connect directly to your organization’s preventative cybersecurity controls. If attackers obtain a password, for example, deploying multi-factor authentication can provide another layer of protection for email, remote access, financial systems, and cloud applications.
Other important ransomware prevention measures include:
Multi-factor authentication
Endpoint protection and monitoring
Regular software and security updates
Email and phishing protection
Strong password policies
Least-privilege access
Regular and tested backups
Employee cybersecurity awareness training
Secure remote access
Network monitoring
Documented incident response procedures
The Canadian Cyber Centre specifically identifies MFA, backups, software updates, and awareness of phishing attempts as foundational cybersecurity practices for Canadian organizations.
No single security tool can guarantee that ransomware will not reach your organization. The goal is to create multiple layers that make an attack harder to execute and easier to contain.
Your Legal and Privacy Obligations May Start During the Incident
A ransomware incident can involve more than encrypted files.
Modern ransomware attacks may involve data theft and extortion as well as encryption. The Canadian Cyber Centre notes that ransomware has evolved to include situations where threat actors steal data and use it for extortion.
If personal information is involved, your organization may also have privacy obligations.
For organizations subject to Canada’s federal private-sector privacy law, PIPEDA requires reporting breaches of personal information when they pose a real risk of significant harm. Organizations must also maintain records of breaches as required by the legislation and guidance.
You can review the Privacy Commissioner’s mandatory breach reporting guidance to understand the federal requirements.
The important point is that privacy and regulatory considerations should be part of your incident response process rather than something the business investigates for the first time after an attack.
Your Backups Need to Be Part of Your Ransomware Recovery Plan
Backups are one of the most important components of ransomware recovery, but simply having a backup service is not enough.
Attackers may attempt to compromise backup systems before encrypting production data. That means businesses need to understand where their backups are stored, who can access them, how they are protected, and whether they can actually be restored.
Ask your IT provider:
When was the last successful backup?
When was the last restore test?
Are backups protected from the main network?
Can an attacker using a compromised administrator account delete the backups?
How quickly can critical systems be restored?
Which systems would be restored first?
Who is authorized to begin recovery?
A backup that has never been tested should not be treated as a guaranteed recovery solution.
What Should Employees Do When They Suspect Ransomware?
Employees are often the first people to notice something unusual.
They may see files suddenly renamed, receive a ransomware message, notice that a shared drive is inaccessible, or realize that an account has sent messages they did not create.
Employees should know exactly who to contact.
Depending on the situation, the initial response may include disconnecting an affected device from the network, securing compromised accounts, contacting the IT or cybersecurity provider, and preserving information that may help determine what happened.
Employees should not assume that deleting a suspicious email, restarting a computer, or attempting to fix the problem themselves has resolved the incident.
The faster a suspected ransomware incident reaches the right person, the sooner the organization can begin containment and investigation.
Test Your Ransomware Incident Response Plan Before an Attack
A plan sitting in a shared folder is not enough.
Businesses should periodically test their ransomware incident response plan through a tabletop exercise. The exercise does not need to be complicated.
For example, imagine that your file server becomes encrypted at 2:00 p.m. on a Friday.
Ask your team:
Who discovers and reports the incident?
Who takes control of the response?
Who has authority to isolate systems?
Who contacts the IT provider?
Who contacts the cyber insurance provider?
How do employees communicate if email is unavailable?
What systems are restored first?
Who determines whether personal information was affected?
Who communicates with customers?
How do you document the incident?
A short exercise can reveal missing contact information, unclear responsibilities, outdated procedures, or backup problems before a real emergency exposes them.
Review our guide on choosing the right cybersecurity tools if your organization’s prevention and protection measures need strengthening alongside your incident response plan.
Why Fraser Valley Businesses Should Act Now
Businesses in Chilliwack, Abbotsford, Mission, Langley, and throughout the Fraser Valley depend heavily on technology to communicate with customers, process payments, manage records, schedule employees, and deliver services.
When those systems become unavailable, the financial impact can extend well beyond the ransom demand.
Downtime can affect:
Employee productivity
Customer service
Payroll
Accounting
Production
Scheduling
Supplier relationships
Confidential information
Business reputation
Regulatory obligations
The Canadian Cyber Centre’s current ransomware assessment emphasizes that ransomware can disrupt operations, supply chains, data, and the services organizations provide.
That makes ransomware preparedness a business continuity issue, not simply an IT issue.
Build Your Ransomware Response Plan Before You Need It
You do not need a 50-page cybersecurity policy to get started.
Create a concise ransomware response plan that identifies your decision-makers, emergency contacts, backup and recovery procedures, communication process, and steps for isolating affected systems.
Then test it.
Review the plan at least annually and whenever your staff, technology, vendors, or insurance coverage changes. Make sure the people named in the plan know their responsibilities and can access the information even if your normal systems are unavailable.
Ransomware cannot always be prevented, but your organization can be better prepared to detect, contain, respond to, and recover from an incident.
For Fraser Valley businesses, the time to build a ransomware incident response plan is before the first suspicious screen appears, not after your systems are already encrypted.